The Magento Guest-Cart Placement Loop: Anatomy of an E-Commerce Exploit
When e-commerce managers evaluate the security of their Magento Open Source storefronts, they typically look for visible anomalies: database defacements, altered administrative credentials, or explicit lines of injected code inside checkout layouts. However, some of the most destructive e-commerce threat vectors operate entirely within standard protocol boundaries. One such vector is the Malicious Guest-Cart Placement Loop.
This automated exploit pattern bypasses standard security filters by manipulating native Magento REST and GraphQL API endpoints. Left unshielded, a guest-cart loop can exhaust server CPU limits, corrupt transaction sequencing, trigger inventory lockouts, and lead to catastrophic store downtime.
Anatomy of the loop: how the attack works
The exploit targets the open layout of the Magento guest checkout pipeline. To provide a frictionless user experience, Magento permits unauthenticated shoppers to generate temporary cart instances, append item configurations, upload shipping metadata, and query payment variables without requiring an authenticated account profile.
An automated botnet exploits this open framework by executing a multi-stage request array:
- Token generation: The bot initiates a POST request to /rest/V1/guest-carts, generating a raw masked cart session token natively within Magento's memory layer.
- Payload injection: The script spikes item parameters into that specific session by calling POST /rest/V1/guest-carts/{cartId}/items.
- The execution loop: The bot issues an aggressive, continuous stream of PUT /rest/V1/guest-carts/{cartId}/order request blocks.
The technical impact of the third stage is severe. Even if the order fails—either because the bot inputs fake credit card information or because the transaction payload is intentionally left empty—the request still forces the Magento core to spin up extensive database lookups, query underlying stock variables, evaluate active rules engines, and process payment module handlers for every line variation. When distributed across hundreds of proxy nodes, this sequence creates a severe resource exhaustion event that slows down real customers attempting to check out.
Technical mitigation: hardening natively and at the edge
Securing your site against an active guest-cart placement loop requires a defense-in-depth framework that handles traffic verification before expensive application layers can process the arguments.
1. Edge layer: Cloudflare WAF and rate limiting
The primary objective of edge mitigation is to filter automated traffic entirely before it reaches your origin server's network cards.
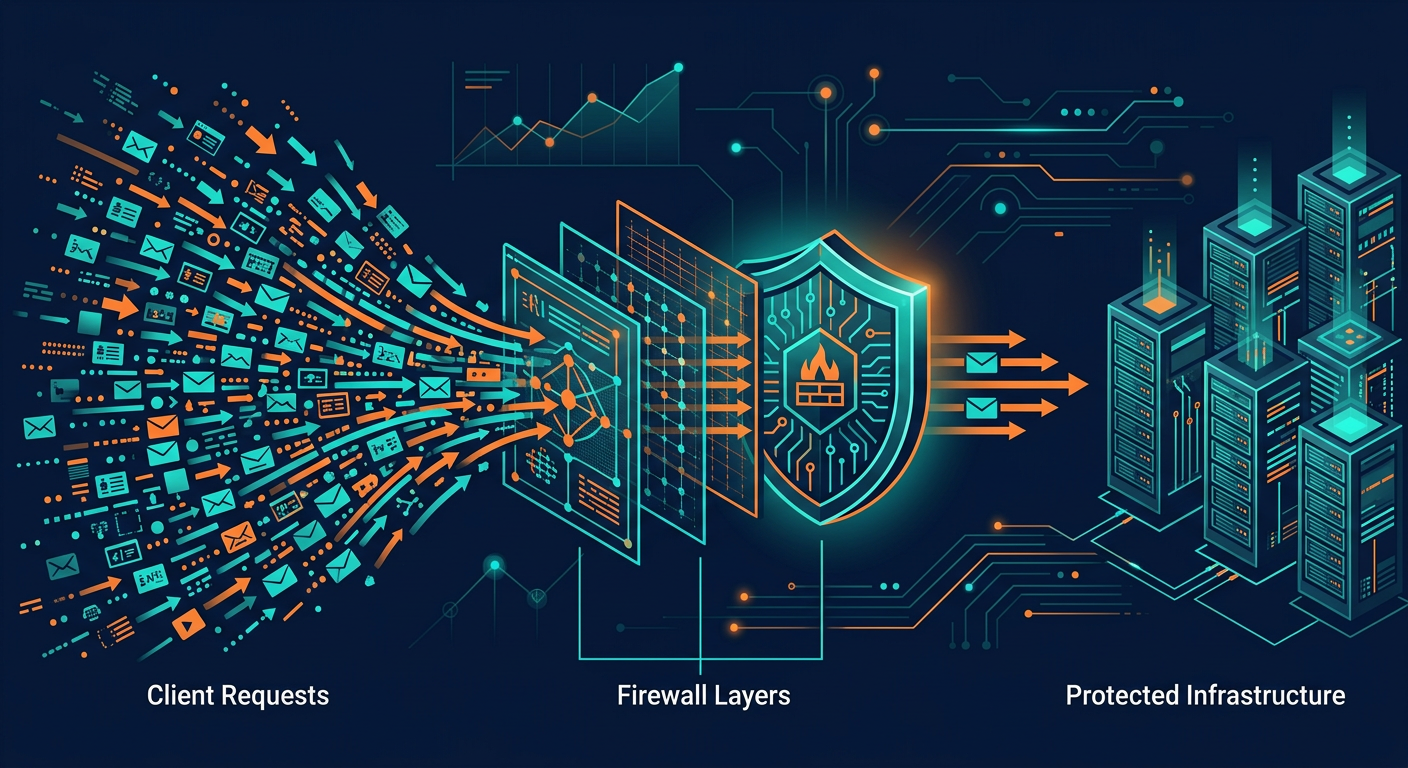
Within your Cloudflare console, configure an advanced Rate Limiting Rule explicitly targeting your store's resting endpoints:
- Target URI pathway: Choose "URI Path Contains" and set it to /rest/V1/guest-carts/.
- Action threshold matrix: Restrict traffic flags to a maximum of 5 requests per minute per individual client IP signature.
- Mitigation action: Set the rule to serve an un-bypassable JavaScript Managed Challenge or a hard network block to immediately isolate headless client scripts while ensuring legitimate shoppers face zero transactional friction.
2. OS gateway layer: Fail2Ban log sentinel automation
If a sophisticated bot manages to mimic a standard browser user-agent and bypass your edge thresholds, your local operating system layer must instantly catch the malicious signature and drop the attacking subnet.
Create a dedicated log sentinel parser profile on your Ubuntu instance:
sudo nano /etc/fail2ban/filter.d/apache-guestcart-loop.confPaste this exact filtering pattern to target malicious API order validation queries:
[Definition]
# Target automated exploit loops attempting to brute-force guest cart placements
failregex = ^<HOST> - - "PUT /rest/V1/guest-carts/\d+/order HTTP/\d\.\d" (200|404|500)
ignoreregex =
Link this filter to an active, un-bypassable UFW (Uncomplicated Firewall) drop rule inside your local /etc/fail2ban/jail.local configuration container:
[apache-guestcart-loop]
enabled  = true
port     = http,https
filter   = apache-guestcart-loop
action   = ufw
logpath  = /var/log/apache2/access.log
maxretry = 3
findtime = 60
bantime  = 86400
This forces Fail2Ban to continuously monitor your active Apache access log pipelines. If a single IP executes more than 3 guest-cart order queries within a 60-second window, its access tokens are immediately revoked, and UFW safely blocks the connection at the kernel layer for 24 hours.
Architectural resilience: preserving business continuity
Securing an enterprise-grade e-commerce application requires looking beyond basic source patches to understand how traffic flows through your entire system layout. Defending against modern multi-vector scraper botnets cannot rest solely on Magento's code layout.
By utilizing edge CDN rules to absorb malicious loops, combined with kernel-level firewall automation to protect server resources, e-commerce operators can ensure their stores remain stable and secure for legitimate buyers around the clock.
EStronghold's Core Care and Managed Care retainers include exactly this kind of layered protection — edge filtering, server hardening, and continuous monitoring. Email [email protected] to book a Magento Security and Operations Assessment.