Increase Ubuntu Linux Server Log Retention Default
Why You Should Increase Ubuntu Server Log Retention Default from 14 to 90 Days
When you spin up a fresh Ubuntu Server, it comes pre-configured with sensible defaults designed to protect your disk space. One of those defaults is managed by logrotate, which typically compresses and deletes your system and web server logs (like Apache or Nginx) after just 14 days.
While a two-week window keeps your storage lean, it leaves a massive blind spot for modern server administration, security auditing, and compliance.
If you are running production workloads—especially e-commerce platforms like Magento or custom web applications—increasing your log retention from 14 days to 90 days is one of the simplest yet most impactful infrastructure upgrades you can make. Here is why.
1. The Reality of Security Breach Detection
According to global cybersecurity benchmarks, the average time it takes an organization to detect a data breach is over 200 days.
Sophisticated attackers rarely break in and cause immediate havoc. Instead, they exploit a vulnerability, establish persistence, and quietly scout your system or exfiltrate data over weeks or months. If an intruder breached your Apache web server 3 weeks ago, a 14-day log retention policy means the evidence has already been permanently deleted.
Bumping your retention to 90 days gives your security team a three-month historical window to perform forensic analysis, track down IP addresses, identify the initial attack vector, and patch the exploit.
2. Spotting Elusive, Intermittent Bugs
Not all software bugs crash your site instantly. Some of the hardest issues to troubleshoot are slow, creeping degradations:
- A memory leak that only triggers under specific traffic patterns.
- A third-party API integration that fails only during end-of-month billing cycles.
- Database deadlocks that happen sporadically.
With only 14 days of data, comparing "normal" system behavior against "abnormal" behavior is incredibly difficult. A 90-day history allows you to look back at previous months to establish baselines, track trends, and catch intermittent errors that slip through two-week cycles.
3. Compliance and Regulatory Requirements
If your Ubuntu server handles user data, financial transactions, or health records, 14 days of logs isn't just risky—it might be illegal.
- PCI-DSS (Payment Card Industry Data Security Standard): Requires keeping audit trail logs for at least one year, with at least 30 to 90 days immediately available.
- GDPR & HIPAA: Demand strict accountability and data tracking capabilities, which heavily rely on robust log retention to prove compliance in the event of an audit or breach investigation.
Failing an audit due to missing log data can result in heavy fines or the revocation of your ability to process credit cards.
4. Better Traffic and User Behavior Insights
Logs aren't just for when things go wrong; they are goldmines for operational intelligence. Web server access.log files track every visitor, bot, and resource request.
- Did a sudden spike in traffic last month correlate with a marketing campaign?
- Is a specific malicious bot scraping your site every 30 days?
- Are old, broken links throwing 404 errors and hurting your SEO?
A 90-day window provides a clean, quarterly view of your traffic patterns, allowing you to optimize your server resources and understand user behavior without relying solely on client-side tools like Google Analytics.
The Trade-off: Storage vs. Visibility
The primary argument against longer log retention is disk space. Ninety days of logs will inherently take up more room than fourteen.
However, because Ubuntu’s logrotate automatically utilizes gzip compression (compress and delaycompress), text-based log files are shrunk down to a fraction of their original size. For most servers, the peace of mind and security coverage gained by keeping 90 days of logs vastly outweighs the minor cost of a few extra megabytes or gigabytes of storage.
How to Make the Switch
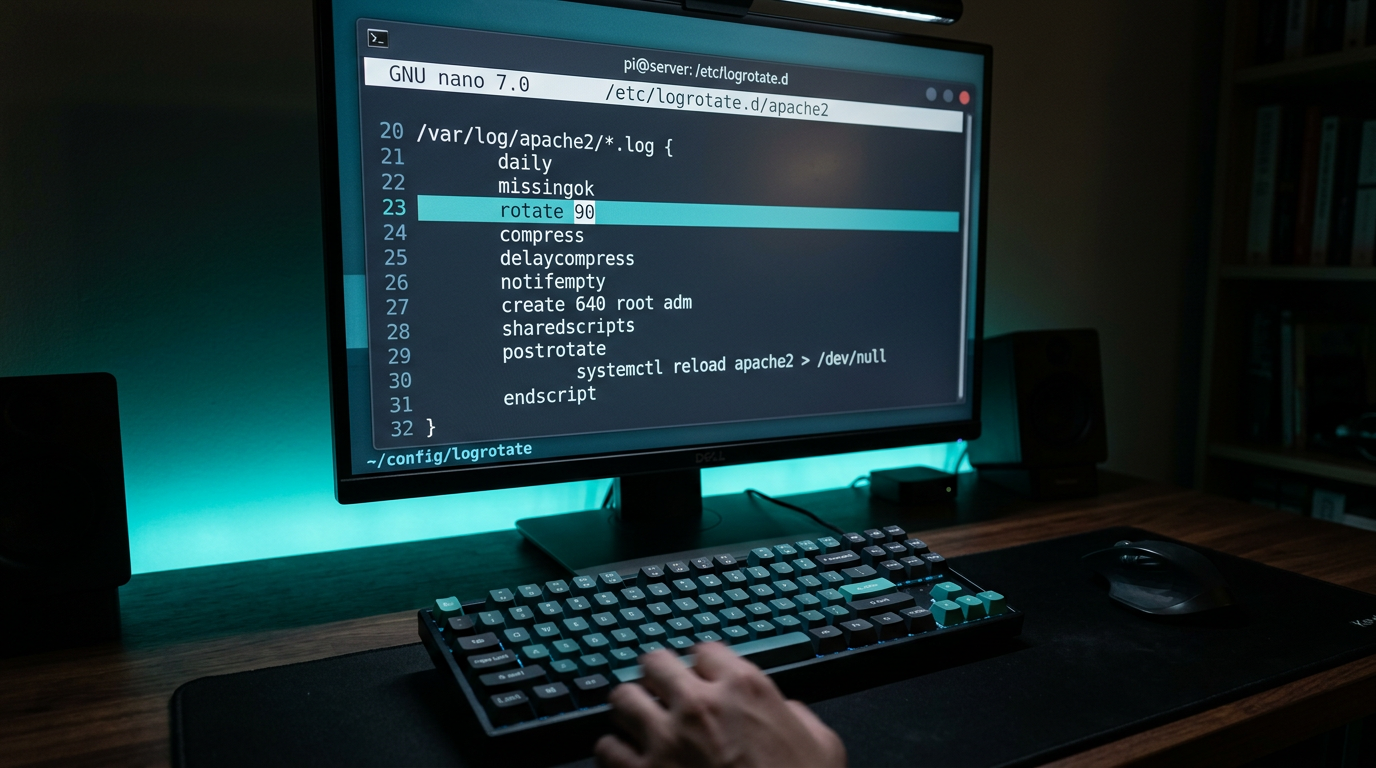
Transitioning is easy. By modifying your configuration files inside /etc/logrotate.d/ (such as the apache2 or nginx blocks), you can simply change the line:
rotate 14
to:
rotate 90
Coupled with a daily rotation setting, your server will seamlessly begin building a comprehensive, 3-month historical archive.
Conclusion
A 14-day log retention policy treats logs as a temporary luxury. A 90-day policy treats logs as what they actually are: critical infrastructure assets. Don't wait for a mystery bug or a security incident to realize your history has been wiped clean. Upgrade your retention today, and give your future self the data needed to protect your server.