What's Onboarding with EStronghold like? in details
What to Expect When You Onboard with EStronghold Inc.: A Deep Dive Into Our Onboarding Process
For e-commerce directors and store owners running Magento Open Source, the transition to a new security and operations partner can feel daunting. You are handing over the keys to your digital storefront—the lifeblood of your business. You might be wondering: Will this disrupt my live checkout? How much technical heavy lifting is required on my end? What exactly happens to my data?
At EStronghold Inc., we believe that world-class security starts with absolute clarity. Our onboarding process is designed to be frictionless, non-destructive, and entirely transparent. We don't guess, and we don't use generic scripts that break your system. Instead, we use a meticulous, structured onboarding protocol to map your digital perimeter and launch your Fortress Security Audit.
Here is exactly what to expect during your onboarding journey with EStronghold.
Phase 1: Corporate & Stakeholder Overview
We begin by establishing a clear line of communication. Security is as much about human coordination as it is about software code.
- The Goal: Define who is who and verify your domain ownership.
- What We Need: Your official registered legal name, primary store domains, and a designated Primary Technical Contact.
By establishing a dedicated technical liaison from day one, we ensure that if we spot an active exploit during our initial sweep, we can reach the right decision-maker instantly without wasting time in corporate telephone loops.
Phase 2: Infrastructure Architecture Mapping
Before we touch a server, we need to understand the precise mechanics of your hosting environment. Magento is a highly complex ecosystem; a setup optimized for an AWS cloud infrastructure behaves very differently from one hosted on Nexcess or DigitalOcean.
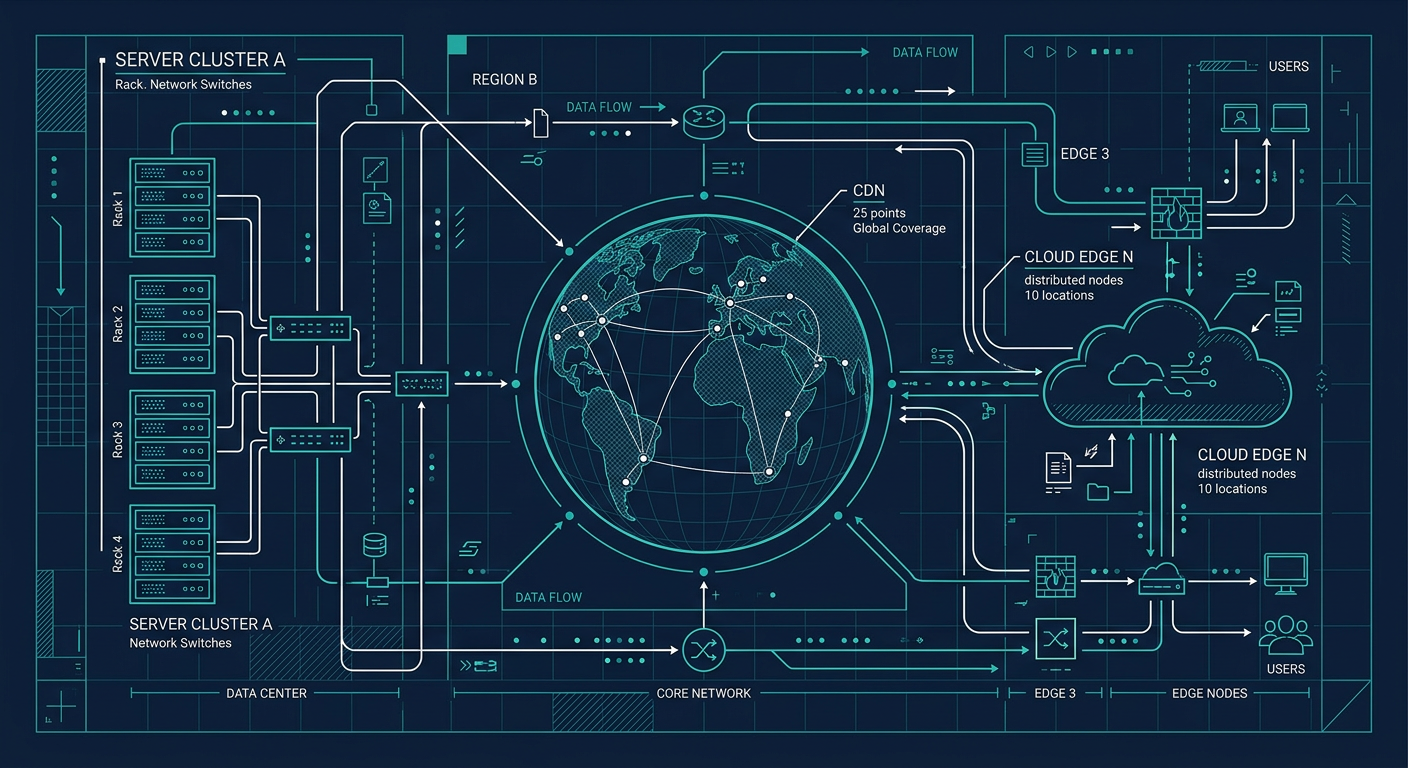
- The Goal: Build an exact blueprint of your hardware and software matrix.
- What We Need: Your underlying operating system (e.g., Ubuntu, Debian, or Rocky Linux), your web server engine (Nginx vs. Apache), and your specific application profile (such as Magento Open Source 2.4.6-p5 running on PHP 8.2).
Knowing these variables allows us to tailor our forensic tools to your specific environment. It guarantees that our diagnostic scans run smoothly in the background without putting a strain on your system resources.
Phase 3: Edge Reverse Proxy & DNS Access Matrix
One of the most common vulnerabilities in Magento stores is origin IP leakage. If a malicious botnet discovers your raw server IP address, they can bypass security layers like Cloudflare entirely and attack your server directly.
- The Goal: Secure and evaluate your global routing layer.
- What We Need: Access to your Edge CDN or DNS management layer (Cloudflare, Sucuri, etc.).
We highly recommend adding our auditor email as a restricted user to your Cloudflare Dashboard under a "Security Read/WAF Edit" baseline. This allows us to inspect your Web Application Firewall (WAF) configurations and bot management settings without requiring your master account password.
Phase 4: Secure Origin Server Access Profiles
To perform a true forensic log pass and file integrity check, we must look under the hood. We do this via encrypted terminal sessions (SSH).
- The Goal: Establish a secure, encrypted pipeline for our engineering team.
- What We Need: Your server's static IPv4 address and SSH port parameters.
We prioritize security at every step. Rather than asking for a password, we highly recommend Public Key Authorization. We provide a specific public key command line string for your team to add to your server's authorized keys file. This grants our workstation access securely and leaves a clear audit trail.
Important Note: All command interactions during this phase are strictly restricted to non-destructive, read-only sweeps. Your production checkout environment will remain completely unaffected.
# Example of the secure authorization command used during onboarding:
echo "ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIKFortressSecurityConsultingAuditorKey" >> ~/.ssh/authorized_keys
Phase 5: Specific Forensic Diagnostic Checkpoints
Every store comes to us with a unique history. To help us focus our investigation, we ask you to flag any unusual application behavior or anomalies observed over the past 30 days.
- What We Look For: Intermittent checkout glitches, unexplained server CPU spikes, sudden waves of headless automated search queries, failed PCI-DSS compliance scans, or rogue administrative usernames in your Magento backend.
By pointing us toward these symptoms, you help our forensic team map active vulnerabilities much faster, pivoting directly to the root cause of your system stress.
Our Chain of Custody & Security Guarantee
We treat your technical infrastructure with the highest level of care. EStronghold operates under a strict Chain of Custody protocol:
[Onboarding Data Received] ──> [Encrypted Read-Only Audit] ──> [Contract Finalization] ──> [Credentials Revoked/Cycled]- Zero Footprint: No production database values are altered or modified during our audit phase.
- Data Isolation: No data snapshots or client files ever leave your server's virtual storage array without explicit, written stakeholder clearance.
- Immediate Revocation: All temporary credentials, encryption keys, and access points provided during onboarding are immediately cycled and revoked upon contract finalization.
Ready to Build Your Fortress?
Onboarding with EStronghold Inc. means moving away from chaotic, reactive firefighting and stepping into a world of proactive hardening and continuous monitoring. We don't just hand you an automated report and disappear. We stand by your side as an ongoing operations partner, keeping your store stable and secure.
Email [email protected] to book a Magento Security and Operations Assessment.