Closing the Origin Loophole: How a Broken Apache Configuration Clears the Way for Magento 2 Layer-7 DDoS Attacks
We frequently audit e-commerce infrastructure that appears bulletproof on paper but remains vulnerable in practice. A classic example occurred recently during an emergency recovery operation for a high-traffic Magento 2.4.6-p15 store running on an Apache2 Ubuntu origin server.
The symptoms were classic: the website was cripplingly slow, intermittently throwing 504 gateway timeouts, and rendering the checkout entirely unresponsive. To the untrained eye, it looked like a standard hardware exhaustion issue. To a security specialist, it was an architectural vulnerability actively being exploited.
Here is the technical post-mortem of how a subtle configuration misalignment allowed a devastating Layer-7 DDoS attack to bypass Cloudflare completely, and the exact steps we took to restore lightning-fast responsiveness.
The Symptoms and Initial Diagnosis
When we were brought in, the server's processing pool was completely saturated. Our first step was checking the raw system stress:
magento_user@origin-server:~$ uptime
 12:44:54 up 1 day,  1:40,  2 users,  load average: 48.15, 32.03, 14.10
A load average of 48 on a multi-core server means the PHP-FPM process pool is drowning. We immediately dumped the active Fail2Ban configuration to check if our local intrusion prevention system was mitigating the load. The server had an impressive defensive matrix of 21 custom jails (including magento-exploits, magento-backdoor, and php-injection).
Yet, the site was still timing out.
We turned to the Apache access logs (/var/log/apache2/access.log) to inspect the incoming traffic patterns. What we found was an aggressive, distributed Layer-7 automated scraper attack targeting resource-intensive Magento endpoints. Hundreds of requests per second were hammering this specific footprint:
114.119.***.*** - - [29/Oct/2026:00:00:21 -0400] "GET /customer/account/login/referer/aHR0cHM... HTTP/1.1" 200 21427 "-" "Mozilla/5.0... PetalBot"
16.216.***.*** - - [29/Oct/2026:00:01:39 -0400] "GET /customer/account/login/referer/...SELECT+COUNT(*)... HTTP/1.1" 200 21847 "-" "Reflectionbot"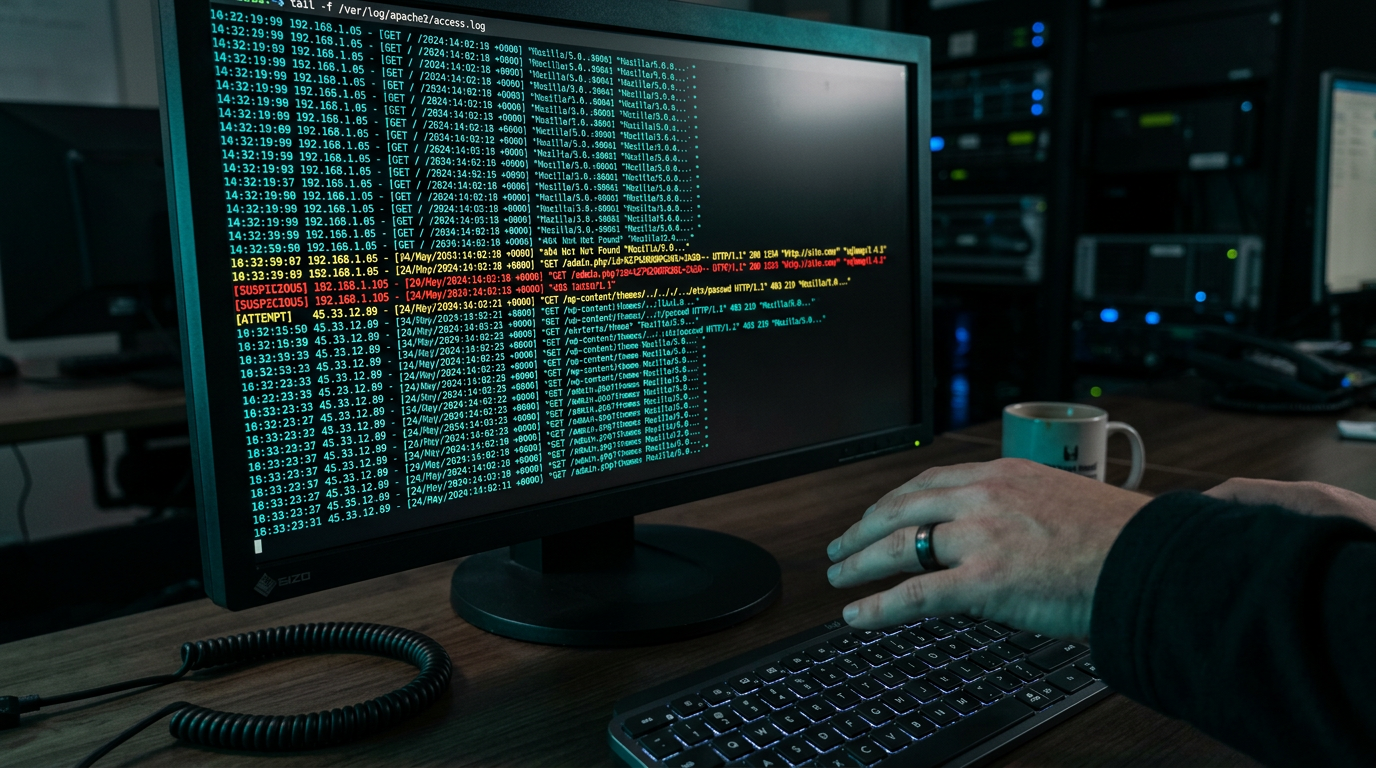
The Configuration Fatal Flaw: The Origin Bypass
Looking closely at the log dump, the fatal architectural flaw became obvious. The IP addresses appearing in the primary remote host column belonged directly to Huawei (114.119.*) and AWS (16.216.*) networks.
Because this environment was supposed to be protected behind a Cloudflare proxy, Apache should have only been receiving connections from Cloudflare's reverse proxy IPs. The presence of raw crawler and hosting provider IPs proved that the attackers had discovered the origin server’s public IP address. They were completely bypassing the Cloudflare Web Application Firewall (WAF), bypassing edge DDoS mitigation, and hitting the Apache web ports directly.
Furthermore, although the administrator had enabled Apache’s remoteip module, it was malfunctioning. Because the connection was bypassing Cloudflare, there was no CF-Connecting-IP HTTP header present in the network payload. Apache fell back to logging the direct socket IP, and Fail2Ban was rendered entirely blind—locally banning random bots while the underlying flood kept hitting the kernel.
Why the Attack Paralysed Magento 2
The attackers explicitly targeted the /customer/account/login/referer/ path. In Magento 2, this endpoint forces the framework to initialize deep application architecture, parse cryptographically encrypted referer blocks, and handle session states.
When a rogue automated bot matrix or an aggressive scraper loops through this URL thousands of times a minute, it spawns endless heavy PHP processes. The PHP-FPM process pool rapidly saturates, CPU cycles max out, database locks begin to queue, and legitimate shoppers are met with devastating timeouts.
The Architectural Remediations
To overcome this emergency and permanently secure the origin network, we executed a three-stage remediation strategy.
Step 1: Repairing the Apache RemoteIP Architecture
We had to guarantee that when legitimate traffic routes through Cloudflare, Apache seamlessly extracts and logs the real visitor IP.
We created an explicit Cloudflare trust configuration under /etc/apache2/conf-available/cloudflare.conf and populated it with Cloudflare's official, verified IPv4 and IPv6 network blocks:
RemoteIPHeader CF-Connecting-IP
RemoteIPTrustedProxy 103.21.244.0/22 103.22.200.0/22 103.31.4.0/22 104.16.0.0/13 104.24.0.0/14 108.162.192.0/18 131.0.72.0/22 141.101.64.0/18 162.158.0.0/15 172.64.0.0/13 173.245.48.0/20 188.114.96.0/20 190.93.240.0/20 197.234.240.0/22 198.41.128.0/17 2400:cb00::/32 2606:4700::/32 2803:f800::/32 2405:b500::/32 2405:8100::/32 2a06:98c0::/29 2c0f:f248::/32
We enabled the configuration via sudo a2enconf cloudflare and ensured the LogFormat directive in apache2.conf used %a (authenticated remote IP) instead of %h.
Step 2: Closing the Hole via UFW Firewall Hardening
The absolute most effective way to eliminate an origin bypass is dropping the malicious traffic at the networking layer before it can even touch Apache or PHP. We rewritten the Uncomplicated Firewall (UFW) rules to achieve an airtight default-deny posture for web ports.
First, we carefully verified that the administrator’s corporate IP addresses were explicitly whitelisted for SSH (Port 22) to avoid a lockout. Then, we ran a structural script to explicitly allow Port 80 and Port 443 traffic ONLY if the source matched an official Cloudflare subnet.
Finally—and most importantly—we appended global drop rules at the absolute bottom of the matching queue:
# Allow Cloudflare subnets dynamically (Iterating through the blocks)
sudo ufw allow from 104.16.0.0/13 to any port 443 proto tcp
# ... [Repeat for all IPv4 and IPv6 ranges on ports 80 and 443]

# Enforce the catch-all drop rules at the bottom of the list
sudo ufw deny 80/tcp
sudo ufw deny 443/tcp
sudo ufw reload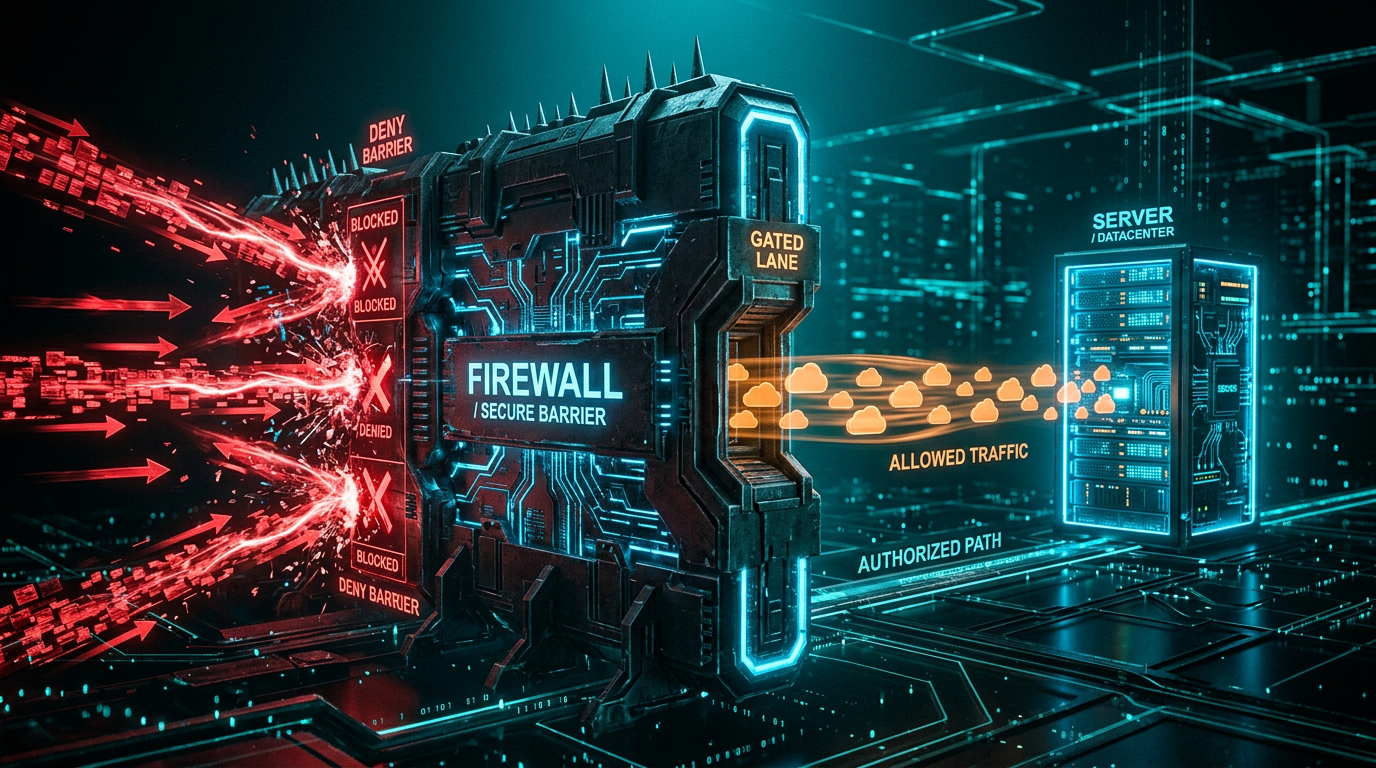
By placing the DENY rules at the absolute bottom, any connection originating from Cloudflare matched an individual allowance rule and passed through. Any direct attacker attempting to slip through via the server's public IP missed the allowance rules, hit the DENY ceiling, and was immediately dropped by the Linux kernel.
The Results
The response from the server was immediate. Within seconds of running sudo ufw reload, the load metrics stabilized dramatically:
magento_user@origin-server:~$ uptime
 12:54:05 up 1 day,  1:50,  2 users,  load average: 0.05, 0.03, 0.00
The system load flatlined to 0.05. A live tail of the access log showed that the chaotic scraper flood vanished completely, leaving behind cleanly parsed internal dummy requests and legitimate visitor traffic utilizing cached static assets. The website returned to normal speeds instantly.
Key Takeaways for Magento Administrators
If you manage a Magento e-commerce storefront protected by Cloudflare, do not assume your origin is safe. Always verify that your server firewall explicitly blocks all non-Cloudflare traffic on HTTP and HTTPS ports. If your architecture allows direct connection to your public IP, an attacker will exploit it, causing fatal slowness that no amount of Magento code caching can fix. Secure your perimeter at the network layer first.