When an Exploit Bypasses Your Perimeter: Fixing PHP CGI Argument Injection on Magento 2
As a Magento store owner or administrator, security is a constant game of cat and mouse. You invest in robust defenses: a Cloudflare Web Application Firewall (WAF), automated hourly scanners like maldetect, and an optimized Apache environment running fail2ban. Your architecture feels impenetrable.
Then you look closely at your raw access.log files and spot a terrifying line:"POST /?-d+allow_url_include%3D1+-d+auto_prepend_file%3Dphp://input HTTP/1.1" 200 417
Your stomach drops. An attacker just attempted a Remote Code Execution (RCE) payload via a PHP-CGI argument injection attack—and your server responded with a 200 OK.
A 200 OK response code means the application didn’t just absorb the traffic; it processed the request, bypassed your perimeter blocks, and interacted with an entry point. This article will dissect what happened behind the scenes, share the hard-learned lessons from this perimeter failure, and provide step-by-step instructions to ensure your server drops these attacks instantly with a 403 Forbidden response.
Understanding the Attack Matrix: Why WAFs Fail
The vector in question targets a structural behavior in how web servers pass traffic to PHP. Historically known as a PHP-CGI query string exploit, the attack relies on sending command-line arguments (like -d or -s) directly inside the URL query string.
When the attacker sends a query like /?-d+allow_url_include=1, they are attempting to dynamically pass configuration switches to the underlying PHP interpreter. If successful, this can force the engine to process external input streams (php://input) as executable code, granting full system control over your Magento workspace.
Many store owners assume that because their primary domain home page works smoothly, their perimeter rules catch everything else. However, automated fuzzers manipulate query string components—such as URL-encoding spaces as + or using hex mutations like %2d for hyphens. If your gateway rule checks only for generic strings, these subtle bypass variations will pass straight through to your backend application, leaving your site dependent entirely on its native PHP configuration to resist execution.
Blueprint for Prevention: Step-by-Step Remediation
To close this loophole, you must implement a defense-in-depth approach. By reinforcing your global PHP configuration, sealing your Apache server gateway, and pushing protective boundaries to the edge via Cloudflare, you eliminate reliance on any single layer of security.
Here is the step-by-step process to permanently secure your perimeter.
Step 1: Enforce a Global Runtime Sandbox in PHP
Your first line of defense is to ensure that even if a request reaches the PHP engine, the runtime variables cannot be altered by query parameters.
Open your web-facing PHP master configuration file using root privileges (replace 8.2 with your active running PHP version):
sudo nano /etc/php/8.2/fpm/php.iniLocate the allow_url_include directive and ensure it is explicitly turned off:
allow_url_include = OffLocate the disable_functions directive and restrict system-level command strings frequently abused by dropped web shells:
disable_functions = exec,passthru,shell_exec,system,proc_open,popen,curl_multi_exec,parse_ini_file,show_sourceNote: Ensure you only apply these restrictions to your FPM pool configuration. Magento's command-line interface requires functions like proc_open to run background tasks via SSH, so keep your CLI profile (/etc/php/8.2/cli/php.ini) unrestricted.
Save the file and restart your PHP-FPM service to apply the environment changes:
sudo systemctl restart php8.2-fpmStep 2: Implement a Rigid Request Filter Shield in Apache
Relying on PHP to safely reject bad instructions is not enough; your web server should drop the connection before it ever reaches the application framework.
Updating your site’s virtual host configuration with an explicit mod_rewrite rule guarantees that query parameters containing hyphens or system file probes are flagged as dangerous traffic.
Open your active SSL configuration file:
sudo nano /etc/apache2/sites-available/yourdomain.com-le-ssl.confLocate your existing RewriteEngine On directives and upgrade your request filter shield to catch hyphen parameters and encoded queries:
# 🛡️ PHP-CGI Parameter Override Shield
# Drops arguments starting with hyphens (-d, -s, %2d) and common parameters before PHP execution
RewriteCond %{QUERY_STRING} ^(%2d|-)[a-z0-9] [NC,OR]
RewriteCond %{QUERY_STRING} (?i)(allow_url_include|auto_prepend_file|allow_url_fopen|php://input)
RewriteRule .* - [F,L]
Verify your configuration structure for syntax errors:
sudo apache2ctl configtestIf the terminal prints Syntax OK, reload the daemon to activate the shield rules:
sudo systemctl reload apache2Step 3: Deploy Custom Cloudflare Edge Controls
To minimize resource strain on your origin server, stop these probes at the edge before they consume network bandwidth or local Apache worker threads.
Navigate to your Cloudflare Dashboard and select your domain.
Go to Security > WAF > Custom rules, then click Create rule.
Toggle the rule editor layout mode to Edit expression and paste the following matching logic:
(http.request.uri.query contains "-d ") or (http.request.uri.query contains "allow_url_include") or (http.request.uri.query contains "auto_prepend_file")Choose Block as the execution action and deploy the rule live.
Verifying Your Defenses
Once these updates are implemented, verify that your defenses are working properly by simulating an attack using a command-line terminal on a separate device.
Execute a simulated query targeting your web server root:
curl -I -k "https://yourdomain"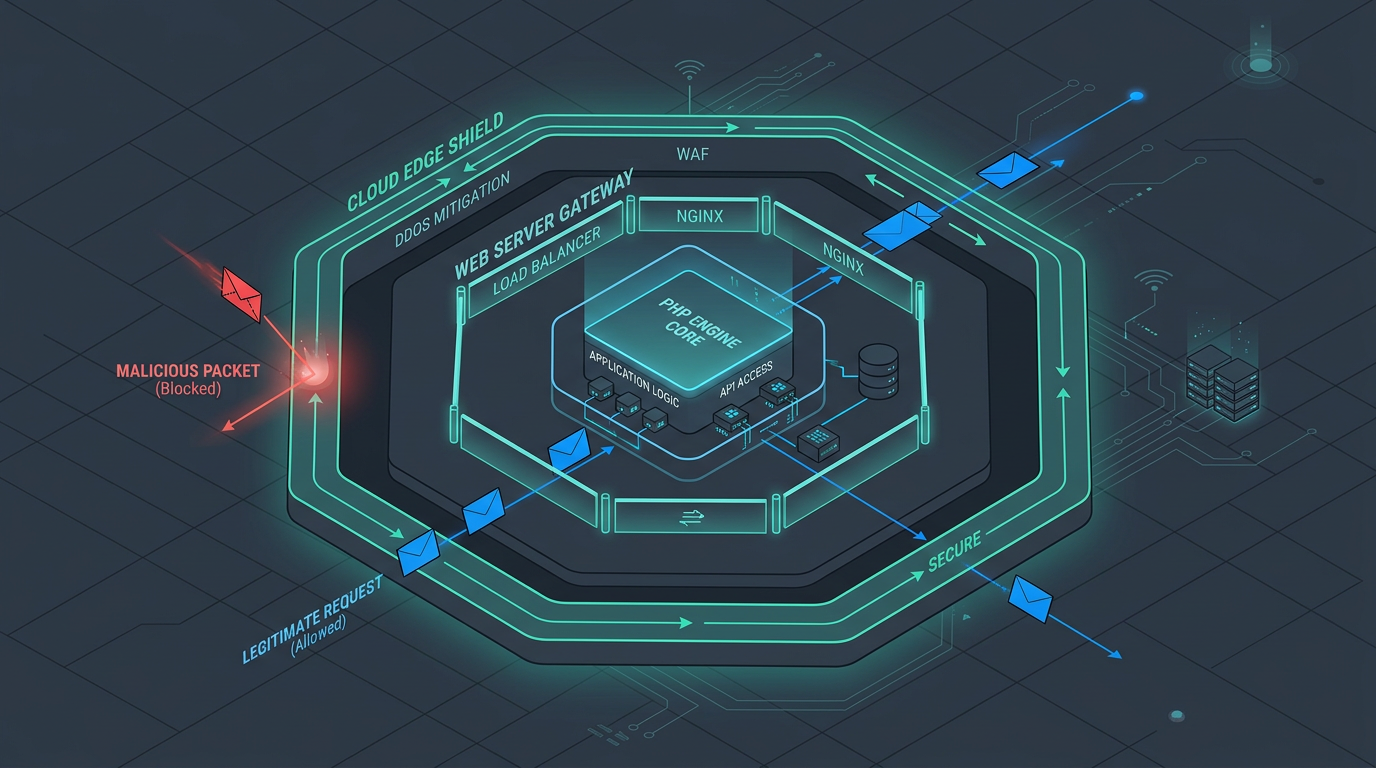
Deciphering the Test Output
The Safe Result: If your configurations are working correctly, your terminal will receive an immediate HTTP/2 403 Forbidden or a Cloudflare drop screen challenge. This indicates that your new layer of security recognized the pattern and blocked it at the gateway.
The Dangerous Result: If you still see an HTTP/2 200 OK response code, your mod_rewrite rules are not executing correctly. Verify that Apache's rewrite engine is active by running sudo a2enmod rewrite, and ensure that your VirtualHost directory blocks allow configuration overrides (AllowOverride All).
Lessons for the Magento Ecosystem
This incident highlights a fundamental lesson in securing e-commerce applications: complacency in automation is a vulnerability. Running automated tools like firewall scanners and basic WAF profiles provides a helpful security baseline, but it doesn't replace manual log audits and defense-in-depth system configuration.
If you discover a past query that bypassed your perimeter and returned a 200 OK, remember these best practices:
Audit Logs for Hidden Errors: Check your Magento var/log/exception.log and var/log/system.log to see if the request caused a core system crash or safely threw a template processing exception.
Scan for Changes in the Web Root: Use commands like find /var/www/html/ -mtime -1 -print to identify any modified system code or unauthorized file uploads within the last 24 hours.
Maintaining a highly performant, secure storefront requires continuous validation. Take the time to audit your server logs, harden your configuration files at the gateway level, and ensure your e-commerce operations remain resilient against automated exploitation.