Top 10 Magento Security Issues with Our Clients' Production Platform
Running a Magento store comes with incredible power and scalability, but its complexity also makes it a prime target for automated attacks. Lately, our engineering team has been responding to an influx of performance degradation and downtime issues. When we dive into the server access logs, the culprit is almost always the same: a mix of aggressive resource-draining bots and targeted exploits.
If your website is running slow or completely crashing, you might not just have a hosting issue—you might be under active attack. Here are the top 10 Magento security issues we are currently seeing across our clients' stores, ranked by their severity and business impact.
1. Remote Code Execution (RCE) via Arbitrary File Uploads
The Threat: This is the most critical issue we’ve encountered. Many merchants rely on custom or third-party extensions to handle features like customer identity validation or order attachments. If these modules don't tightly validate file extensions, attackers can upload executable scripts.
In recent logs, we caught a malicious payload being uploaded to a custom address upload directory:
POST /customer/address_file/upload HTTP/1.1" 200
GET /0cfa054e0573.php HTTP/1.1" 200
The Impact: A 200 OK status code on a newly created .php file means the attacker successfully executed a "web shell" on the server. This gives hackers absolute application-level access to steal databases, inject credit card skimmers, or modify core code.
2. SQL Injection (SQLi) Request Flooding
The Threat: Attackers love targetting native search routing. Bots automatically scan your store by injecting malicious database commands right into the search queries, trying to manipulate database logic or force backend delays using functions like pg_sleep.
We regularly see patterns hitting native endpoints like this:
***.***.144.205 - - "GET /catalogsearch/result/index/?q=acquisitionywi63q3y+or+14+select+149+form+pg_sleep+15 HTTP/1.1" 200The Impact: While modern core Magento applications naturally parameterize queries to prevent data leaks via SQLi, the sheer calculation required to process these long, complex database instructions maxes out MySQL/Mariadb CPU cycles. This instantly locks up your database and brings down site speed for actual shoppers.
3. Application-Layer Denial of Service (DoS)
The Threat: Unlike network-level DDoS attacks that flood your bandwidth, application-layer DoS attacks target server software processes (like PHP-FPM and Nginx). Rogue vulnerability scanners and aggressive scrapers fire continuous, parallel loops of requests against heavy application endpoints.
***.***.46.247 - - "GET / HTTP/1.1" 302
***.***.46.245 - - "GET / HTTP/1.1" 302
The Impact: PHP can only handle a set number of concurrent requests at one time. When a bot cluster hogs every single available execution slot, legitimate checkouts and product browsing attempts are dropped, resulting in 502 Bad Gateway errors.
4. Credential Stuffing & Auth Interface Abuse
The Threat: Malicious scripts use automated lists of millions of stolen username/password combinations (harvested from older breaches across the web) and test them rapidly on your login endpoints.
***.***.214.127 - - "POST /customer/account/loginPost/ HTTP/1.0" 302The Impact: Beyond eating up processing memory via constant authentication validations, if an administrator or customer has reused a compromised password, their account is hijacked instantly.
5. Sensitive Information Disclosure Prone to Harvesting
The Threat: Sophisticated crawlers systematically look for standard development and infrastructure file layouts. They check if configuration baselines like /.env, /config.json, or local cloud workspace paths are left sitting openly in the public web root directory.
***.***.159.175 - - "GET /.env HTTP/1.1" 404The Impact: Even if your server drops a 404 Not Found for these requests, leaving a deployment backup file exposed by mistake can give attackers immediate access to database keys, encryption salts, and payment gateway tokens.
6. Automated Directory Traversal & CMS Fingerprinting
The Threat: Broad-spectrum scanners don't initially care that you're running Magento; they throw wide nets searching for vulnerabilities across any platform. They parse paths like /wp-content/plugins/ or /administrator/components/ to figure out what software is running on your server.
***.***.132.251 - - "GET /wp-content/plugins/forminator/readme.txt HTTP/1.1" 404The Impact: This creates a massive spike in error logging and traffic noise. If you happen to be running an unpatched WordPress blog or old script suite in a subdirectory alongside your Magento app, your entire store could be compromised through the secondary application.
7. Unprotected REST API Endpoint Abuse
The Threat: Magento's native REST API endpoints, such as /rest/V1/guest-carts/, are critical for modern checkout functionality. However, bots frequently target these routes to test for flaws in API configuration logic.
***.***.238.32 - - "PUT /rest/V1/guest-carts/549/order HTTP/1.1" 400The Impact: If left entirely exposed to high-frequency automated traffic without proper endpoint filtering, attackers can strain cart processing systems or exploit order submission flows.
8. Backups and File Archive Exposure
The Threat: When developers run manual code patches or database backups, they sometimes leave historical variations lying around inside the public root folder (e.g., wp-config.php.backup or db.sql). Attackers run scripts designed exclusively to hunt for text extensions and zip wrappers.
***.***.46.247 - - "GET /wp-config.php.backup HTTP/1.1" 302The Impact: If a scanner successfully hits a legitimate older archive file, the attacker gains immediate access to the structural framework blueprint of your site, making deep target exploits trivial.
9. Server-Side Request Forgery (SSRF) Parameters
The Threat: Malicious scanners attempt to manipulate internal URL parameters, injecting local loopback addresses (like cloud metadata endpoints http://169.254.169) directly into search strings or external rendering windows.
***.***.203.31 - - "GET /?url=http%3A%2F%2F169.254.169.254%2Flatest%2Fmeta-data%2F... HTTP/1.1" 200The Impact: If your software infrastructure processes outbound data requests without explicitly sanitizing the targets, attackers can trick your server into acting as a proxy to read secure cloud metadata or scan your private internal backend architecture.
10. Complete Lack of Core Rate Limiting
The Threat: Many clients come to us running high-spec servers that are completely unprotected by a Web Application Firewall (WAF) or backend rate-limiting layers. This allows basic python and curl script tools to crawl millions of pages without facing any challenges.
***.***.120.20 - - "GET /.env HTTP/1.1" 301 "python-requests/2.34.2"The Impact: Real human shoppers end up competing for CPU time with aggressive scraping bots. Because a single bot can mimic hundreds of visitors per minute, your store slows down to a crawl, tanking your conversion rates and search rankings.
How to Protect Your Store
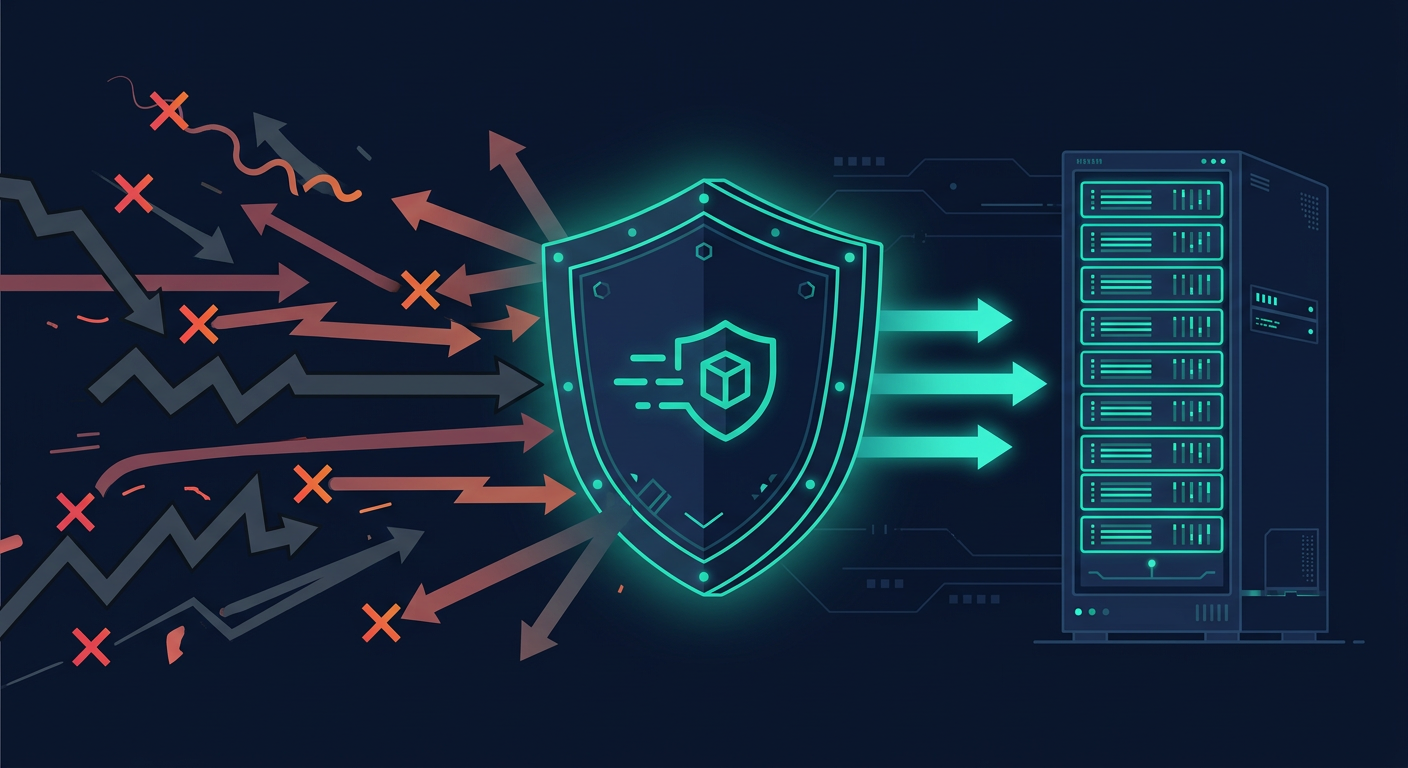
If your access logs look similar to these examples, defensive action is required immediately. Cleaning up a slow site requires stopping the noise before it hits your application:
- Deploy a Cloud WAF: Routing traffic through a firewall like Cloudflare or Sucuri stops bad bots and malicious payloads before they ever reach your origin server.
- Review Custom Code Uploads: Ensure any route handling user uploads strictly filters allowed file extensions via white-lists, and never allow uploaded files to execute directly in the upload path.
- Establish Strict Rate Limiting: Restrict heavy endpoints like /catalogsearch/ and /customer/account/loginPost/ so individual IPs cannot slam your app with unnatural frequencies.
Want to know if your infrastructure is safe? Let us help you review your configuration:
- What hosting platform or server architecture does your Magento store currently run on?
- Have you checked your Magento Admin Panel for unauthorized user accounts or unrecognized modifications?
Email [email protected] for a review of your access logs and security configuration.